

Intune AI agent that answers device questions in Teams and Slack, and runs the fix after approval.
Laptops fall out of compliance, phones get lost, and every one of those becomes a ticket for someone who opens Intune. Workativ looks up the device, replies in Microsoft Teams or Slack, and carries out the action once the right person approves.
IT Teams of all sizes trusts Workativ AI to automate IT Operations & Support

Most device tickets ask something Intune already knows, and the ones that need action wait for an admin.

Device questions go to the service desk
Why am I blocked, where is my app, is my laptop ready: each becomes a ticket for someone who opens Intune.

Lost devices wait for a person
A lost-phone report sits in a queue while the phone stays signed in. Locking needs an admin at a keyboard.

Copilot in Intune is built for admins
Microsoft documents it as an admin tool, so employees have no route to ask about their own device.
People ask about their own laptop or phone in chat, and the reply comes from its Intune record.
Replies name the policy or setting involved. Anything that changes a device waits for the person who should approve it.
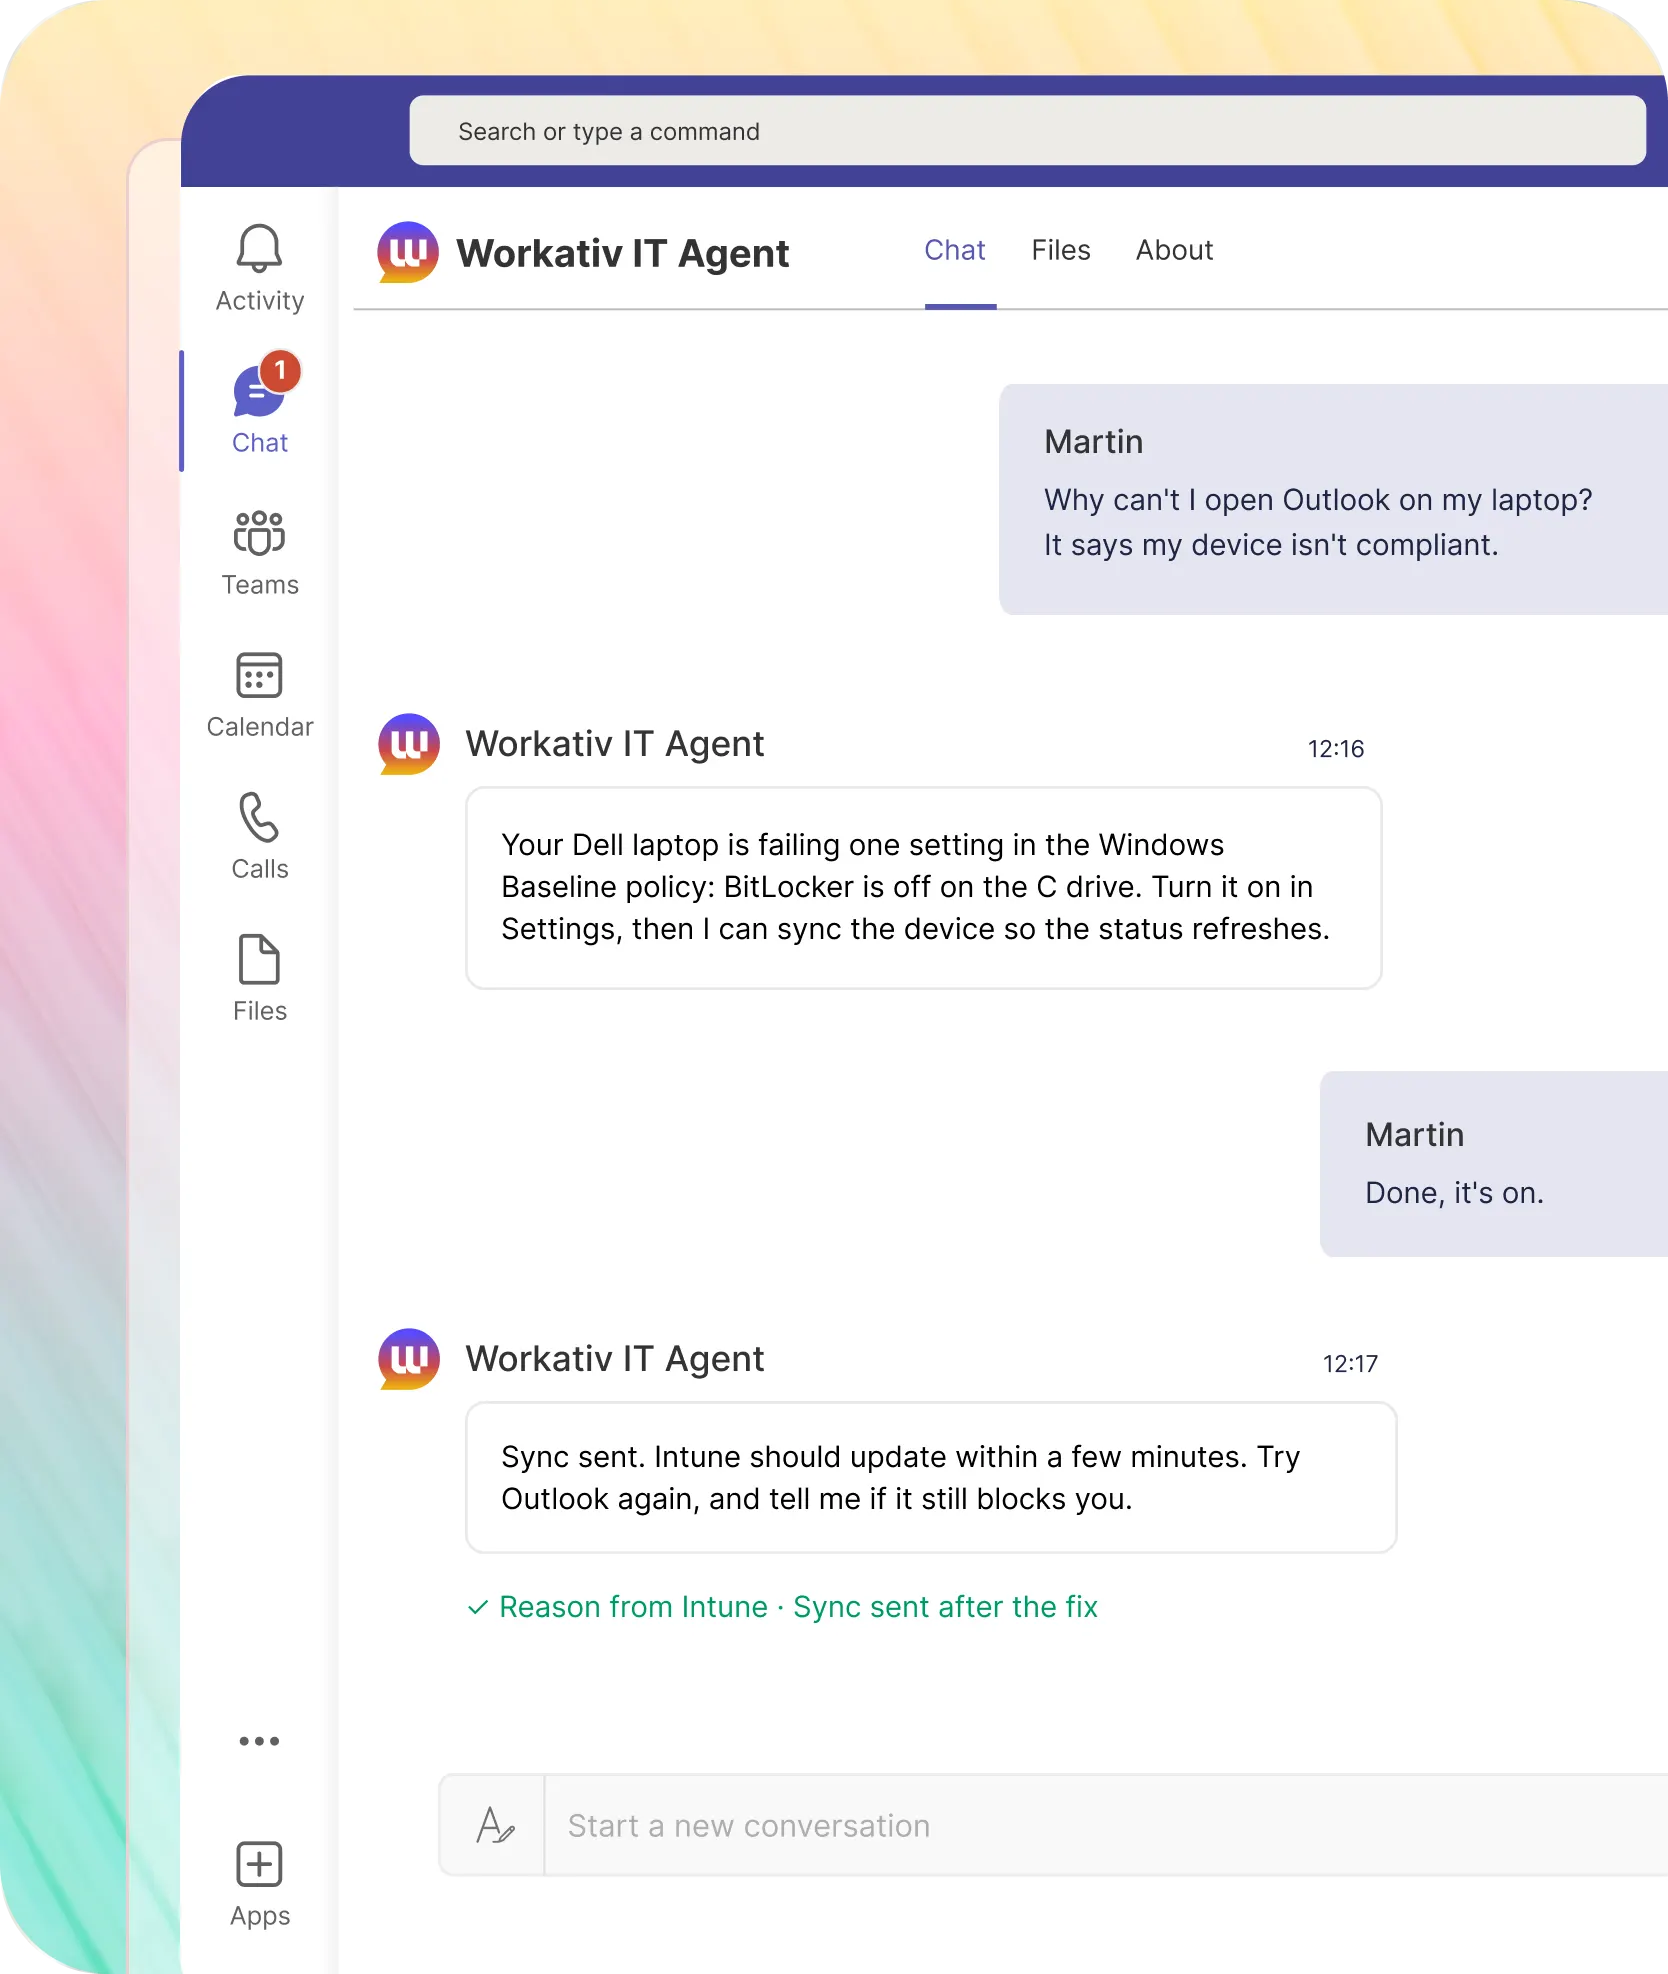
An employee asks why the laptop is blocked, and the reply names the failing setting from Intune.

The reply names the policy and the setting that failed, not just "non-compliant"
A sync is offered when the fix is already in place on the device
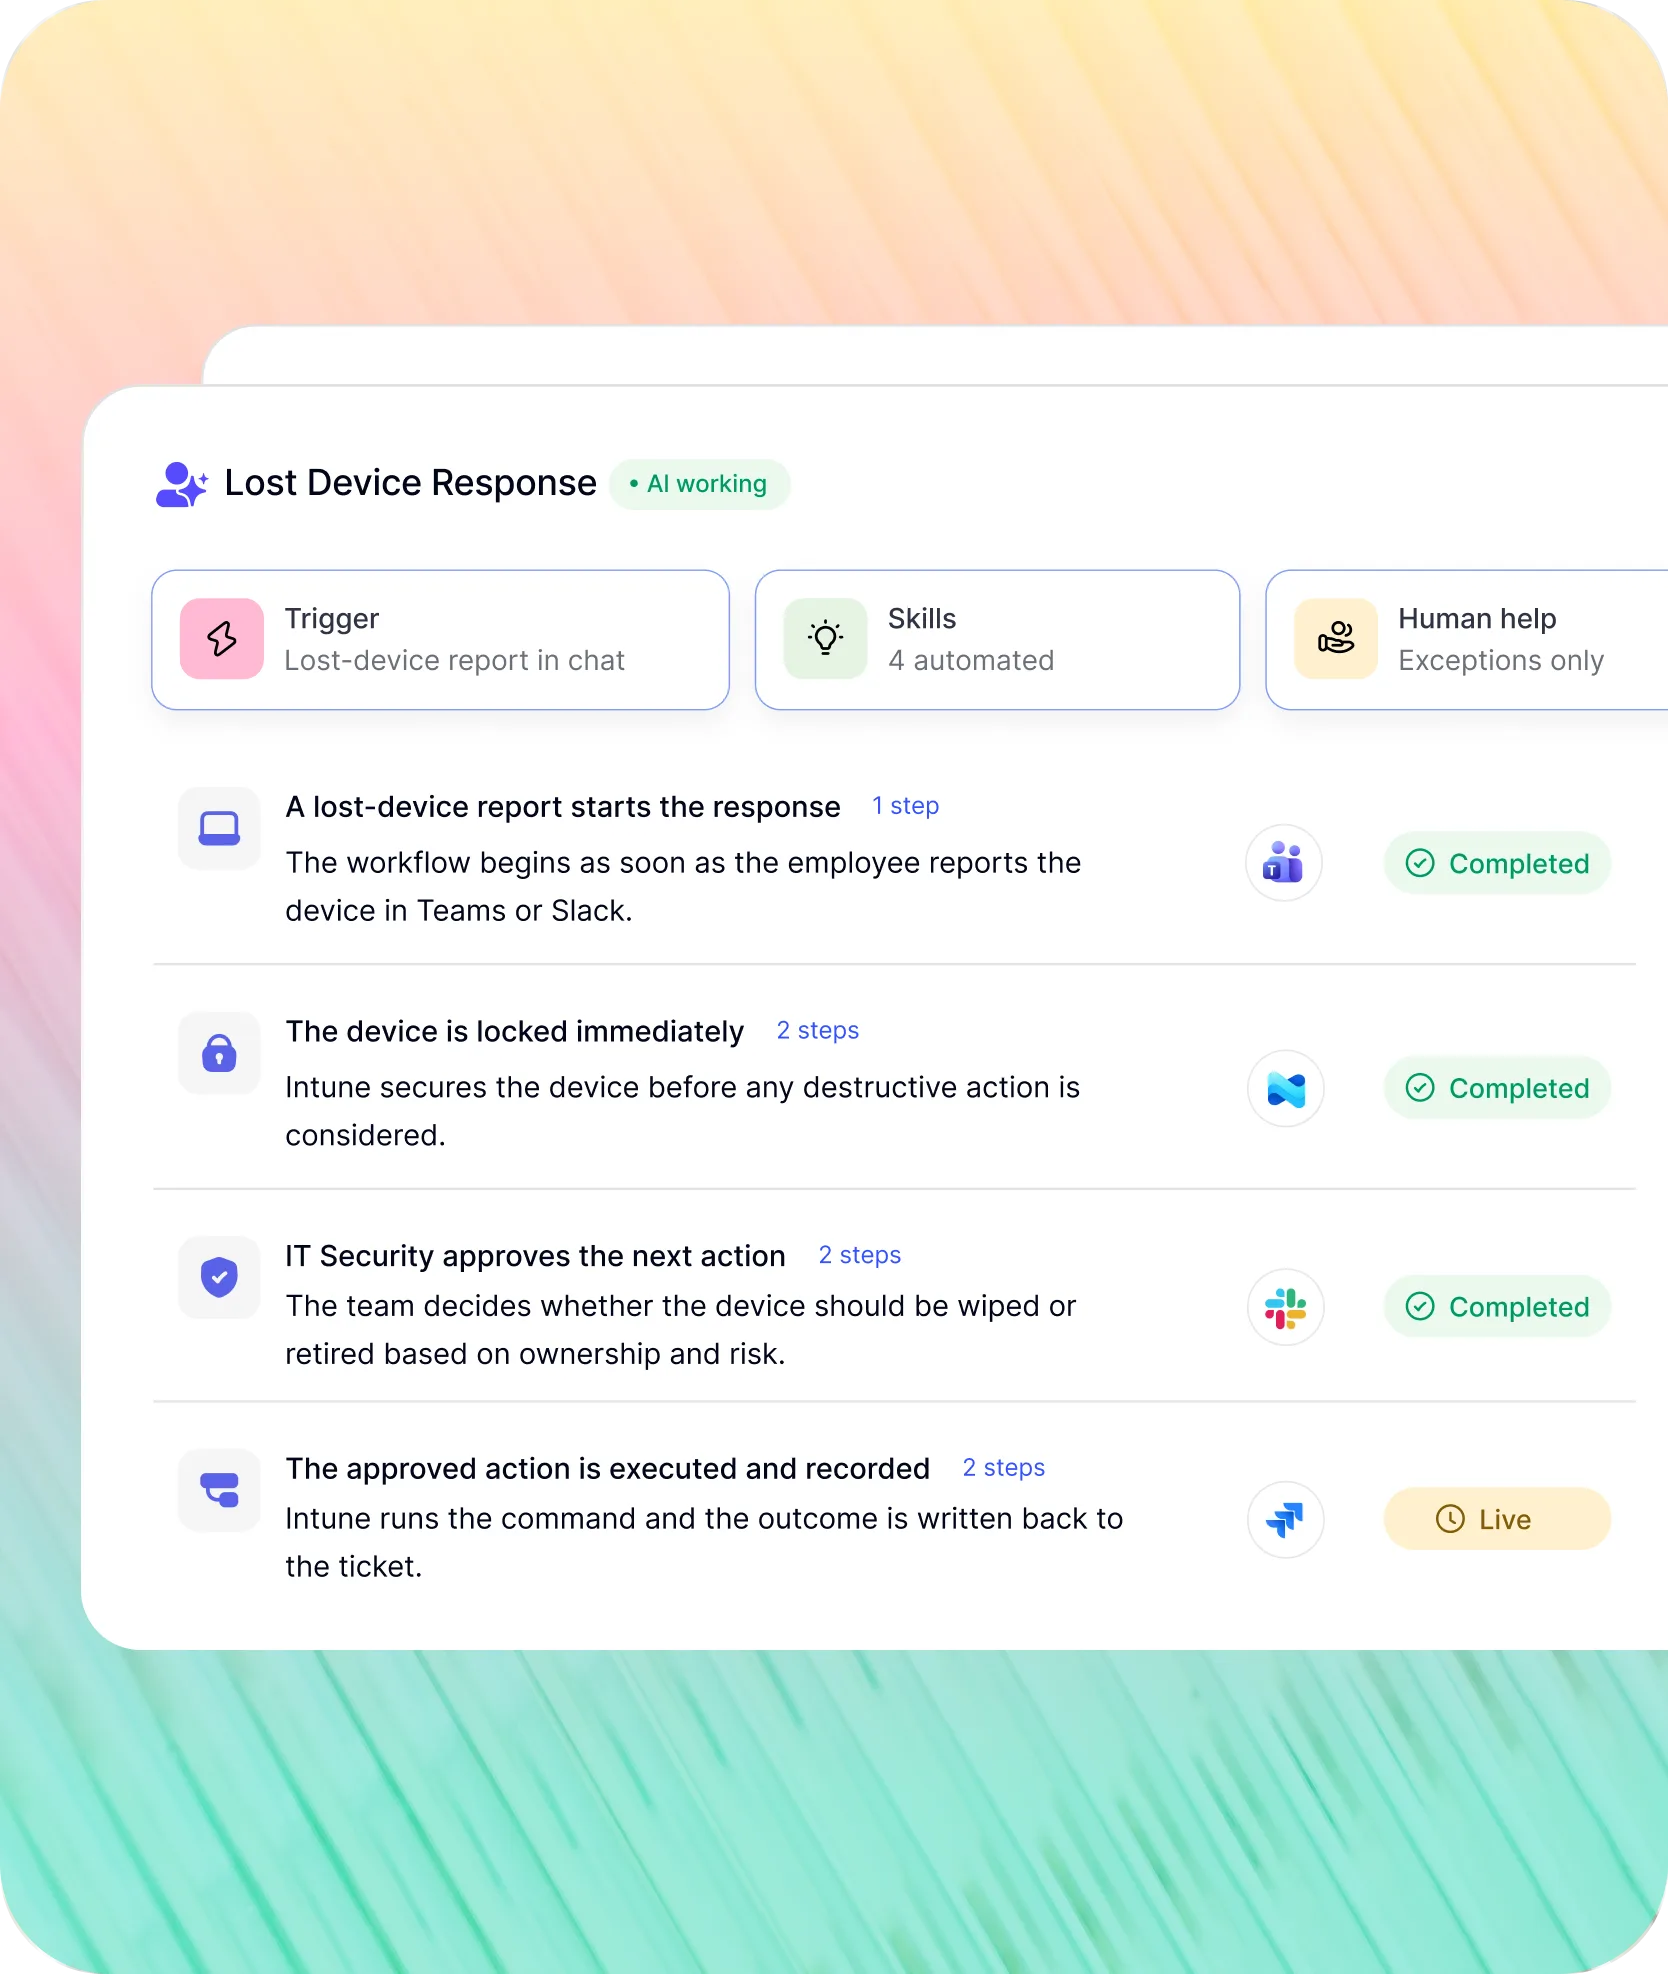
Lost devices, stalled compliance, leavers and stale records follow a routine, so the routine can run on its own.
An event or a schedule starts each one. People are asked in Teams or Slack, and nothing destructive runs without sign-off.
Before day one, the laptop is confirmed enrolled, in the right groups and compliant.
IT gets a short ready or not-ready note per hire
A missing group or failed enrollment is raised before the start date
NMDC runs its IT support in Teams, and 78% of its IT tickets close without an engineer.
"Workativ has been with us every step of the way. From our first IT support use case to HR, and soon Procurement. The platform grows with us, and so does the team behind it. It's rare to find a solution that's both powerful and genuinely easy to manage."

Imran Abid
IT Operations Leader · NMDC Group
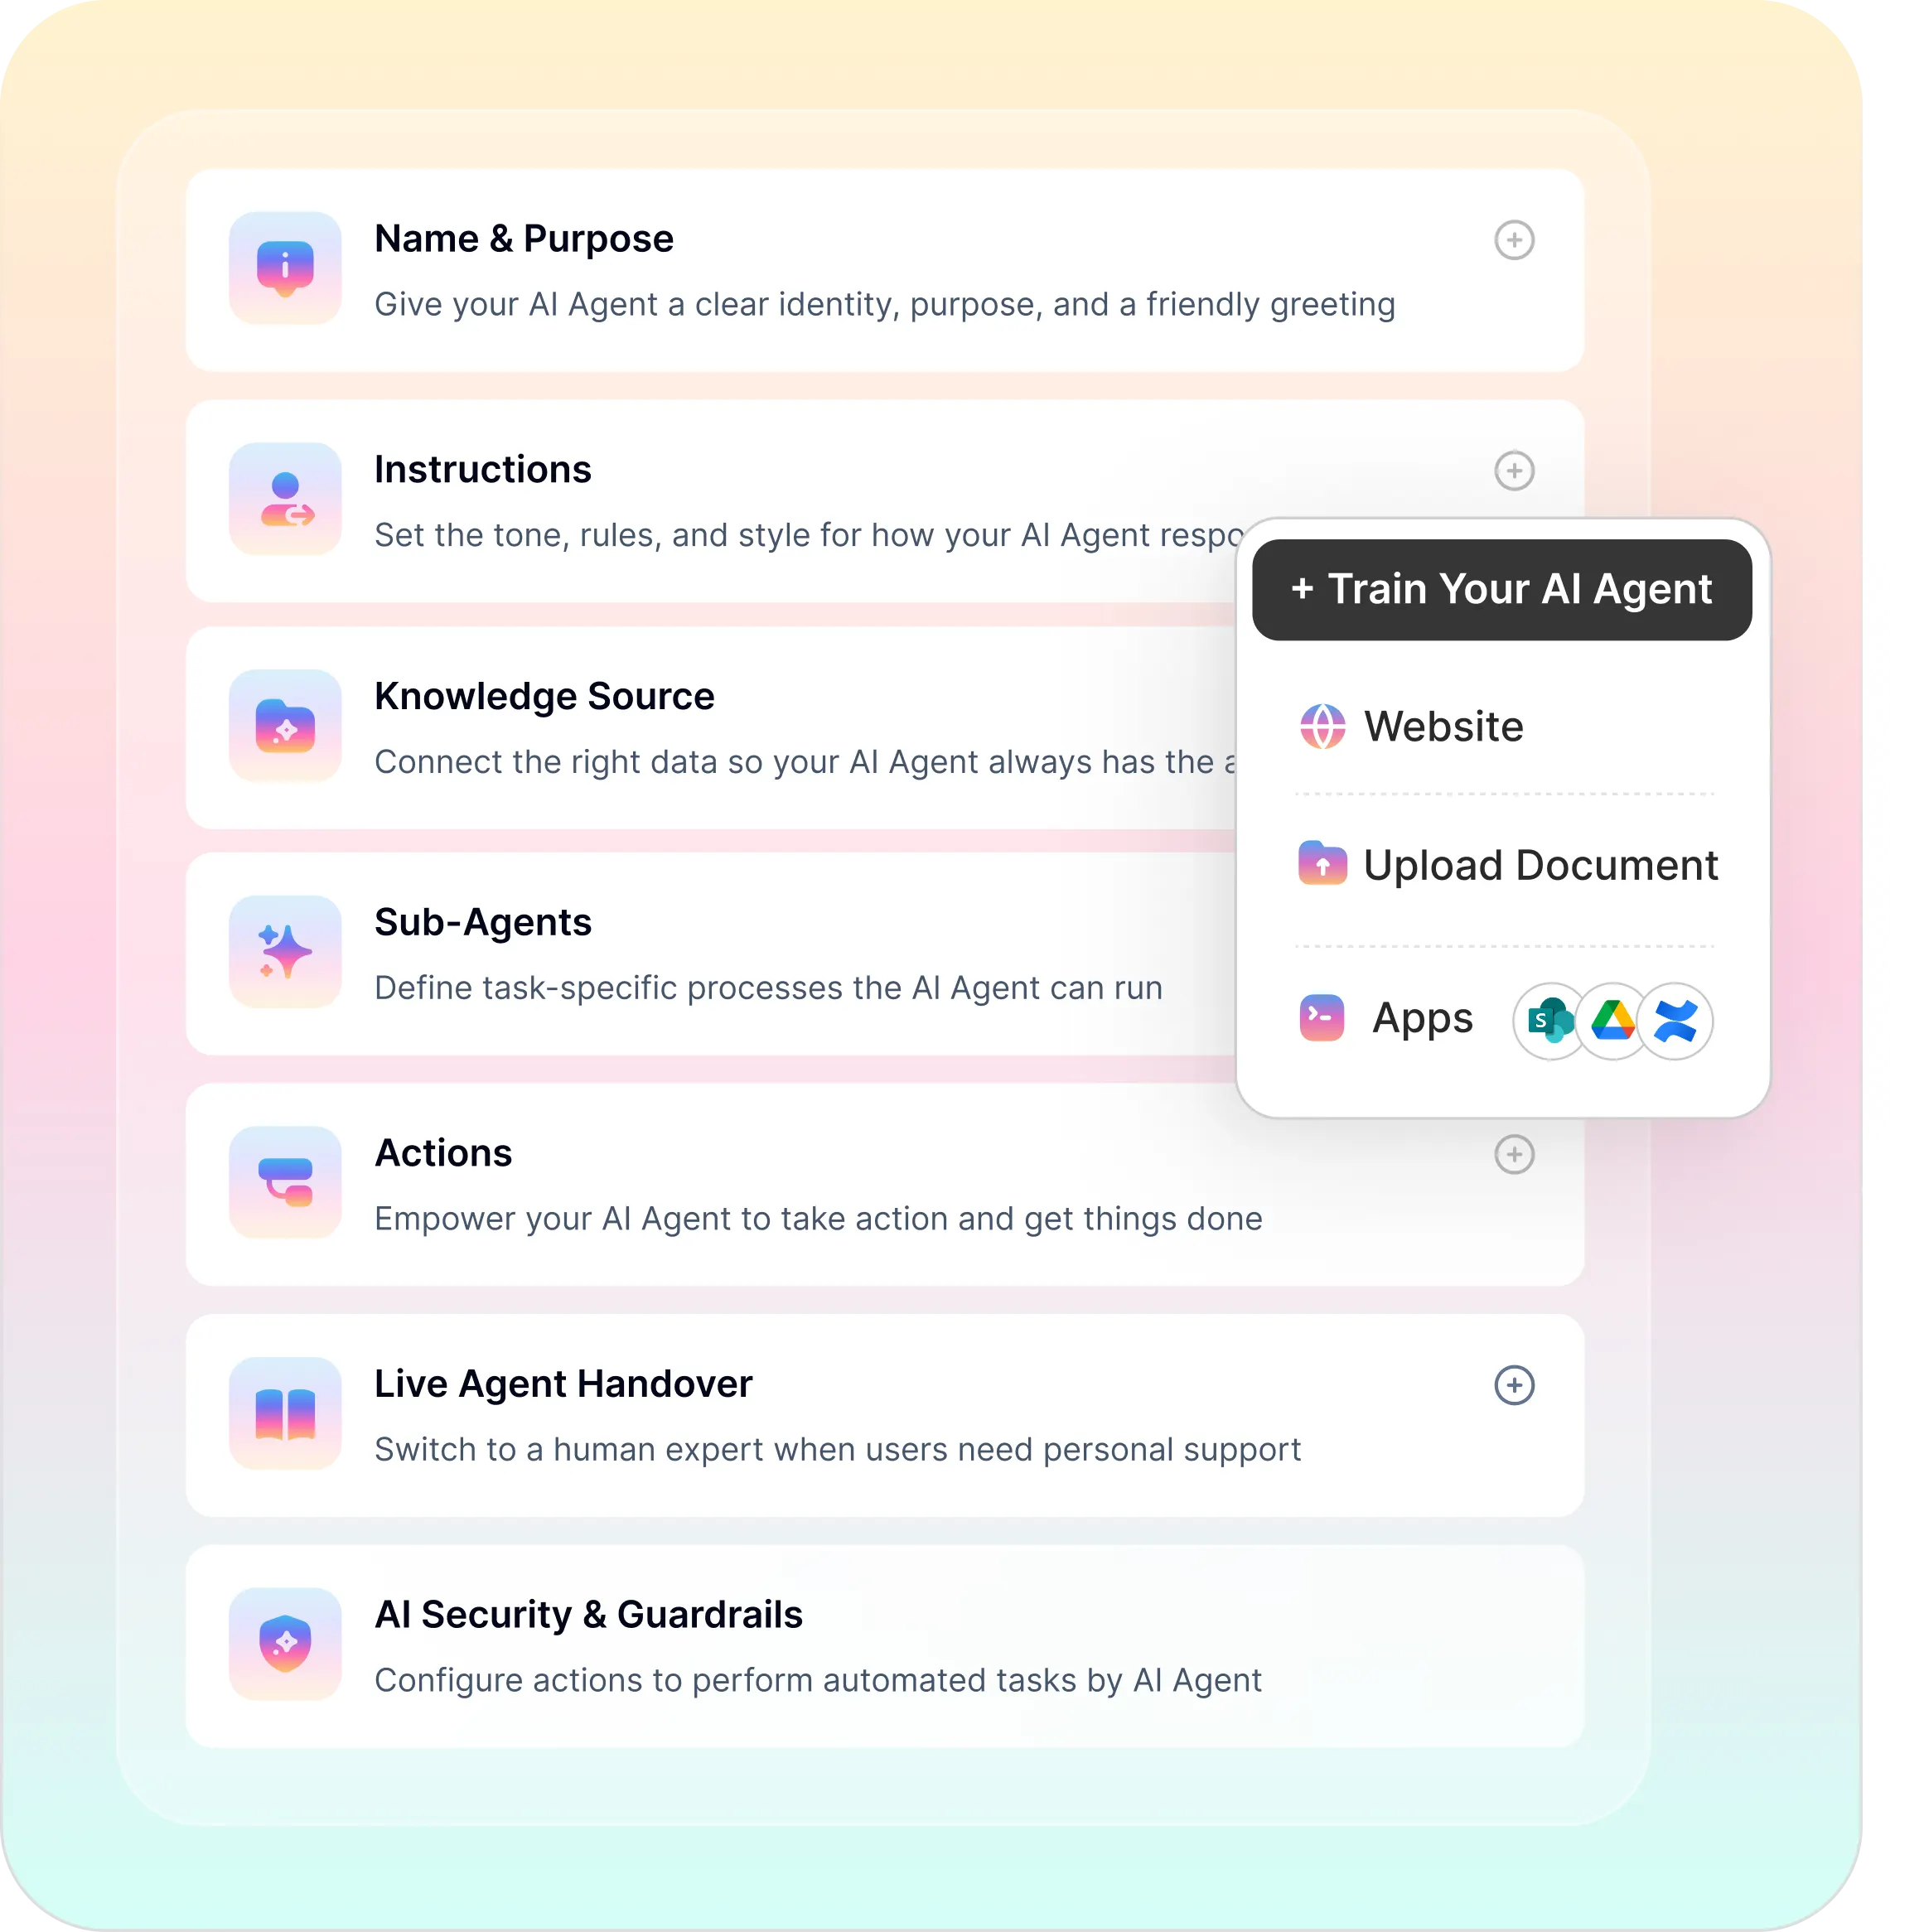
Deploy an Intune AI agent in three steps.
Intune keeps the device records and the rules. Workativ lets employees ask about them and act on them.
You decide the actions, the groups and the approvers, and each run is on record.
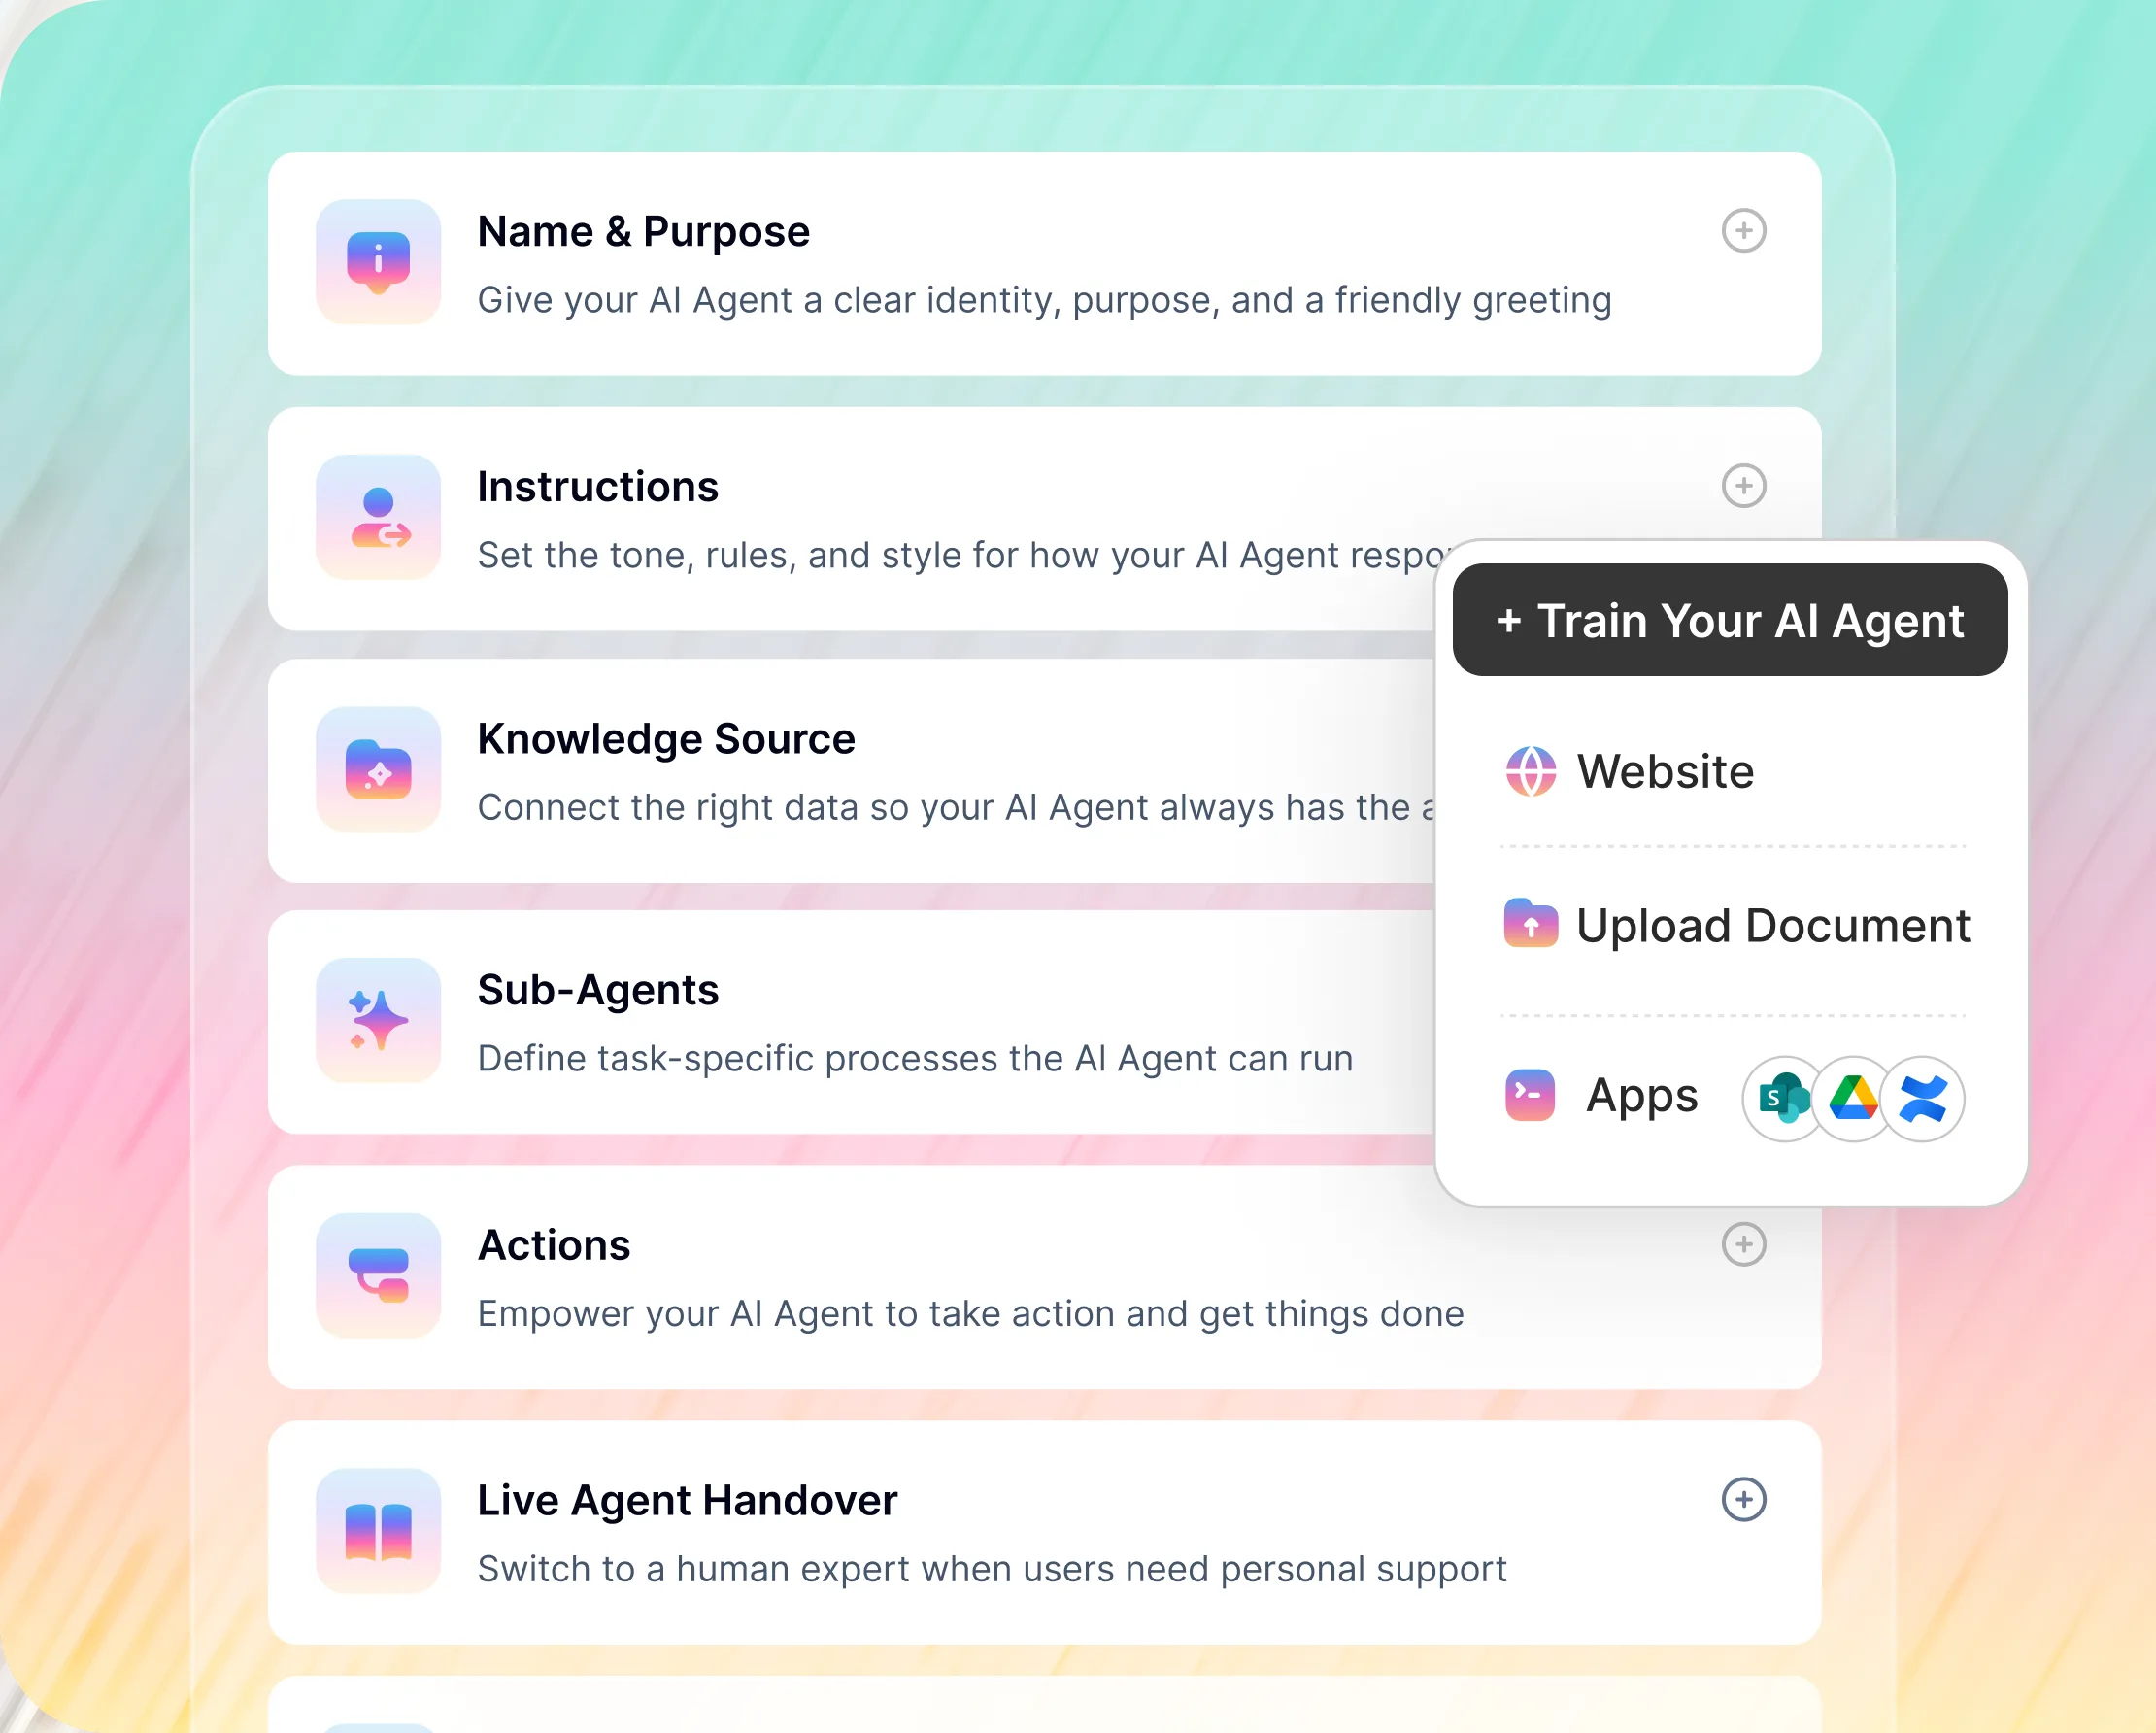
No-Code Builder for Your Intune AI Agent
Choose which device questions and actions the agent handles
Set which groups of users may use each action
Add an approver to any action that changes a device
Copilot in Intune and an Intune AI assistant in chat, compared.
Microsoft built Copilot for the people who run Intune. Workativ is for the people who use the devices, and for the actions that follow their questions.
What matters to IT |  |  |
|---|---|---|
Who uses it |  | Intune admins, in the admin center |
What it answers | | Fleet questions in plain language, KQL for device query, policy summaries |
Acting on a device | | Agents recommend: change review, stale-device offboarding, policy settings, vulnerability fixes |
How access is decided | | |
Beyond Intune | | Microsoft security data through Security Copilot |
Employee self-service | | Not described in Microsoft's documentation |

If your problem is admins searching a large fleet and writing device queries, Copilot in Intune does that job and respects Intune roles. Workativ makes sense when employees need answers about their own device, or when the answer should lead straight to an approved action. Many teams would run both.
Intune holds the device. Your other systems hold the person, the ticket and the approval.
One device answer can draw on Entra ID for the user, Microsoft 365 for the license, and your ITSM for the record.


%20--%3e%3csvg%20version='1.1'%20id='Layer_1'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%20512%20512'%20style='enable-background:new%200%200%20512%20512;'%20xml:space='preserve'%3e%3cstyle%20type='text/css'%3e%20.st0{fill:%23F7F7F7;}%20.st1{fill:%2328E4C3;}%20.st2{fill:url(%23SVGID_1_);}%20.st3{fill:url(%23SVGID_2_);}%20%3c/style%3e%3ccircle%20class='st0'%20cx='256'%20cy='256'%20r='245.5'/%3e%3cg%3e%3cg%3e%3cpath%20class='st1'%20d='M304.7,405.6'/%3e%3c/g%3e%3c/g%3e%3cg%3e%3cg%3e%3cpath%20class='st1'%20d='M305.8,353'/%3e%3c/g%3e%3c/g%3e%3clinearGradient%20id='SVGID_1_'%20gradientUnits='userSpaceOnUse'%20x1='388.1461'%20y1='99.0534'%20x2='204.4846'%20y2='204.5899'%20gradientTransform='matrix(1%200%200%20-1%200%20514)'%3e%3cstop%20offset='0.18'%20style='stop-color:%230052CC'/%3e%3cstop%20offset='1'%20style='stop-color:%232684FF'/%3e%3c/linearGradient%3e%3cpath%20class='st2'%20d='M119.9,330.3c-3,4.9-6.4,10.7-9.3,15.3c-2.6,4.4-1.2,10,3.1,12.7l60.7,37.4c4.4,2.7,10.1,1.3,12.9-3%20c0,0,0.1-0.1,0.1-0.1c2.4-4.1,5.6-9.3,9-15c24-39.7,48.2-34.8,91.9-14l60.2,28.6c4.7,2.2,10.2,0.2,12.4-4.4c0-0.1,0.1-0.2,0.1-0.3%20l28.9-65.4c2-4.7,0-10.1-4.7-12.2c-12.7-6-38-17.9-60.7-28.9C242.6,241.2,173.1,243.7,119.9,330.3z'/%3e%3clinearGradient%20id='SVGID_2_'%20gradientUnits='userSpaceOnUse'%20x1='613.0198'%20y1='1773.9866'%20x2='429.3116'%20y2='1879.5697'%20gradientTransform='matrix(-1%200%200%201%20736.83%20-1676.71)'%3e%3cstop%20offset='0.18'%20style='stop-color:%230052CC'/%3e%3cstop%20offset='1'%20style='stop-color:%232684FF'/%3e%3c/linearGradient%3e%3cpath%20class='st3'%20d='M392.1,181.9c3-4.9,6.4-10.7,9.3-15.3c2.6-4.4,1.2-10-3.1-12.7l-60.7-37.4c-4.3-2.9-10.1-1.7-13,2.5%20c-0.1,0.2-0.2,0.4-0.3,0.6c-2.4,4.1-5.6,9.3-9,15c-24,39.7-48.2,34.8-91.9,14l-60-28.5c-4.7-2.2-10.2-0.2-12.4,4.4%20c0,0.1-0.1,0.2-0.1,0.3L122,190.2c-2,4.7,0,10.1,4.7,12.2c12.7,6,38,17.9,60.7,28.9C269.4,271,338.9,268.4,392.1,181.9z'/%3e%3c/svg%3e)


%20--%3e%3csvg%20version='1.1'%20id='Layer_1'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%20512%20512'%20style='enable-background:new%200%200%20512%20512;'%20xml:space='preserve'%3e%3cstyle%20type='text/css'%3e%20.st0{fill:%23EB3C00;}%20.st1{fill:%23FFFFFF;}%20%3c/style%3e%3ccircle%20class='st0'%20cx='256'%20cy='256'%20r='245.5'/%3e%3cpath%20class='st1'%20d='M152.2,332.7v-152L286.7,131l73.1,23.4V359l-73.1,22L152.2,332.7l134.4,16.2V171.9L199,192.4v119.8L152.2,332.7%20z'/%3e%3c/svg%3e)


%20--%3e%3csvg%20version='1.1'%20id='Layer_1'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%20512%20512'%20style='enable-background:new%200%200%20512%20512;'%20xml:space='preserve'%3e%3cstyle%20type='text/css'%3e%20.st0{fill:%230062FF;}%20.st1{fill:%23FFFFFF;}%20%3c/style%3e%3ccircle%20class='st0'%20cx='256'%20cy='256'%20r='245.5'/%3e%3cpath%20class='st1'%20d='M256,162.5l-91,58.2l91,58.2l-91,58.2l-91-59.1l91-58.2l-91-57.3l91-58.2L256,162.5z%20M164.1,355.5l91-58.2%20l91,58.2l-91,58.2L164.1,355.5z%20M256,278.1l91-58.2l-91-57.3l91-58.2l91,58.2l-91,58.2l91,58.2l-91,58.2L256,278.1z'/%3e%3c/svg%3e)


Enterprise-grade security for IT environments where data protection is non-negotiable.
Put an Intune AI agent in
AI agent in Teams and Slack.
Device answers from Intune, with the fix run after approval. Live in 3–5 days.
Frequently asked questions
Frequently asked questions about the Intune AI agent
What is an Intune AI agent?
An Intune AI agent takes device questions from employees in Microsoft Teams or Slack, looks up the answer in Intune, and can run an action on the device, such as a sync or a remote lock. Workativ's version puts an approval step in front of anything destructive, and writes every action to a log.
Is an Intune AI assistant the same as Copilot in Intune?
No. Copilot in Intune is Microsoft's assistant for admins, powered by Security Copilot, and it answers fleet questions inside the Intune admin center. An Intune AI assistant from Workativ lives in Teams or Slack and is aimed at the person who owns the laptop or phone. Some teams use both: Copilot for the admin's own analysis, Workativ for everyone else.
What can employees ask it?
Why a device shows as not compliant, whether an app is assigned to them, whether a new laptop has finished enrolling, what IT can see on a personal phone, and how to report a lost one. The agent reads that device's record in Intune and replies in plain words, with the fix when there is one.
Which actions can it run on a device?
Sync, restart, remote lock and app assignment on request, and retire or wipe behind an approval, which covers an Intune remote wipe for a lost phone. These are the remote actions Intune already has in its console. You choose which of them are switched on, and for which groups of users.
How does Workativ connect to Intune, and what permissions does it need?
Through an app registration in your Entra tenant that calls Microsoft Graph. Reading devices and compliance needs read permissions only. Wipe and retire sit behind a separate privileged-operations permission, DeviceManagementManagedDevices.PrivilegedOperations.All for wipe, which you grant only if you want those actions in chat.
Does it work with Multi Admin Approval?
Yes. Intune's Multi Admin Approval can protect wipe, retire and delete, and Microsoft applies it to app-based Graph calls as well as to admins in the console. A request from the agent then waits for a second admin, and the requester still has to complete the action once it is approved. Chat approval and Multi Admin Approval can run one after the other.
When does it retire a device, and when does it wipe it?
It reads the ownership field in Intune. A personal device gets a retire, which removes company data and settings and leaves personal data alone. A company-owned device can get a wipe, which restores factory settings. The employee is told which one applies before anyone approves.
What happens when someone loses a device?
The employee reports it in chat, the agent locks the device, and the Intune remote wipe is queued for the approver. Microsoft limits a tenant to 500 wipes and 1,000 retires a day, counted across the console, bulk actions and Graph calls, so a mass request is checked against that before it runs.
Do we need Security Copilot to use it?
No. Copilot in Intune is part of Security Copilot and is measured in security compute units, according to Microsoft's documentation. Workativ does not use that capacity, and it works with Intune on its own. If you already run Security Copilot, the two sit side by side.
What is the difference between an Intune chatbot and an Intune AI agent?
A chatbot answers a question and stops. An agent reads the device record, decides what applies, runs the action after approval, and logs it. Workativ's older Intune chatbot page covers the question-and-answer side, and this page covers the agent.
How long does deployment take?
Three to five days for most teams. The app registration is quick. Most of the time goes on deciding which actions to allow, who approves them, and testing against a handful of real devices, the way an Intune helpdesk would pilot a change.
Which chat platforms does it support, and what can we measure?
Both Teams and Slack work alike. The dashboard shows the questions asked most, the actions run, how many were approved or declined, and which devices keep coming back as non-compliant. Logs can go to your SIEM.